
Home > Case Studies
Case study
Valid credentials became a payroll attack path. Mitiga reconstructed the timeline and restored payment-change functionality with telemetry proof.
Attackers got in. They got nothing.
Campaign
Payroll Pirate
Attack Path
Okta → Workday
Products
Helios AIDR · IR services
Read Time
6
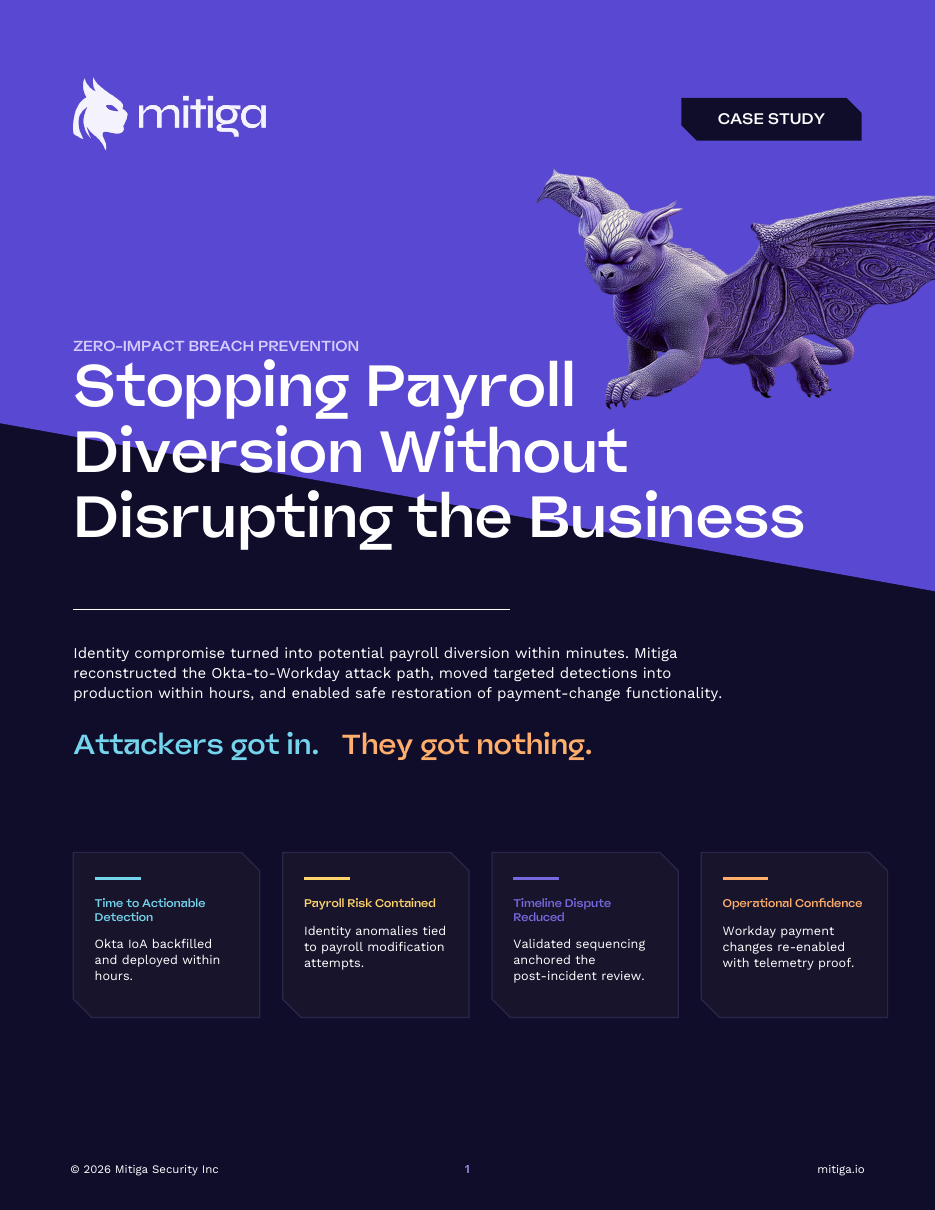
Time to actionable detection
Okta IoA backfilled and deployed within hours.
Payroll risk
Identity anomalies tied to payroll modification attempts.
Timeline dispute reduced
Validated sequencing anchored the post-incident review.
Operational confidence
Workday payment changes re-enabled with telemetry proof.
The pattern was clear and repeatable: failed Okta login attempts, a successful new-device sign-in, a rapid pivot into Workday, and attempted changes to direct deposit or payment election details.
The attacker did not exploit a misconfiguration. They logged in with valid credentials and moved directly toward monetization.
Identity teams, application teams, containment owners, and a real-time scribe moved in parallel during escalation.
Mitiga built an Indicator of Attack for one source IP targeting multiple Okta accounts. Thirty days of activity were backfilled, and the detection moved into production within hours.
Mitiga restored Workday log visibility, resolved processing blockers, and brought sign-on and user activity into one investigative view with Okta anomalies.
A detailed write-up correlated identity and payroll telemetry, confirmed containment timing, and clarified who did what and when.
“Your write up was instrumental in helping us validate the timelines.”
Post-incident review feedback
Mitiga provided panoramic visibility across identity and payroll systems, decoded the attack path into a validated timeline, and enabled decisive containment without disrupting payroll operations.
Companion PDF
The same story, formatted for sharing with leadership. Opens in Mitiga’s PDF viewer — no form, no gate.


