Platform
Solutions
Resources
Company

Agents run across cloud, SaaS, and identity at machine speed. So does Mitiga. It watches agents at runtime and stops the rogue ones before they impact the business.
Let them come.


OLD WORLD
Every agent you approved – and dozens you never knew existed – are reading your data, calling your APIs, and acting through identities you issued. Visibility and compliance tools show you they exist. None show you what they did, in runtime.
NEW WORLD
Mitiga’s AI Agent Security starts where agent discovery stops: the moment an agent acts. Across cloud, SaaS, and identity, Mitiga sees the full chain – prompt to tool call to impact – and steps in before the business feels it.

AI agents are a new actor operating in your environment. Existing security tools can’t see them.
 01
Agents act through borrowed identities, so their actions are hard to trace.
 02
Prompt injection and tool poisoning target agents, and existing tools don’t see them.
 03
Agent behavior shifts from task to task, so anomaly detection is a challenge.
 04
Detection and response have to move at machine speed too.


Every agent – sanctioned, third-party, shadow – inventoried with its connectors and identities, tracked end to end, not in a silo.

Static scans show what was true at your last snapshot. Mitiga catches drift and privilege escalation in real time, the moment it happens.

Behavioral detection for agents, not prompts or endpoints – stops AI agent attacks at machine speed across cloud, SaaS, and identity.

Mitiga revokes the token, quarantines the identity, and reverses the change – contained at the agent, not the account, with minimal blast radius.
Mitiga AI Agent Security goes beyond inventory and compliance to deliver real business outcomes, everywhere your agents act.
While other tools stop at inventory, risk, and compliance, Mitiga’s Zero-Impact Breach Prevention platform sees every agent, decodes what it did, and stops and contains AI agent attacks before business impact.
See everything as one
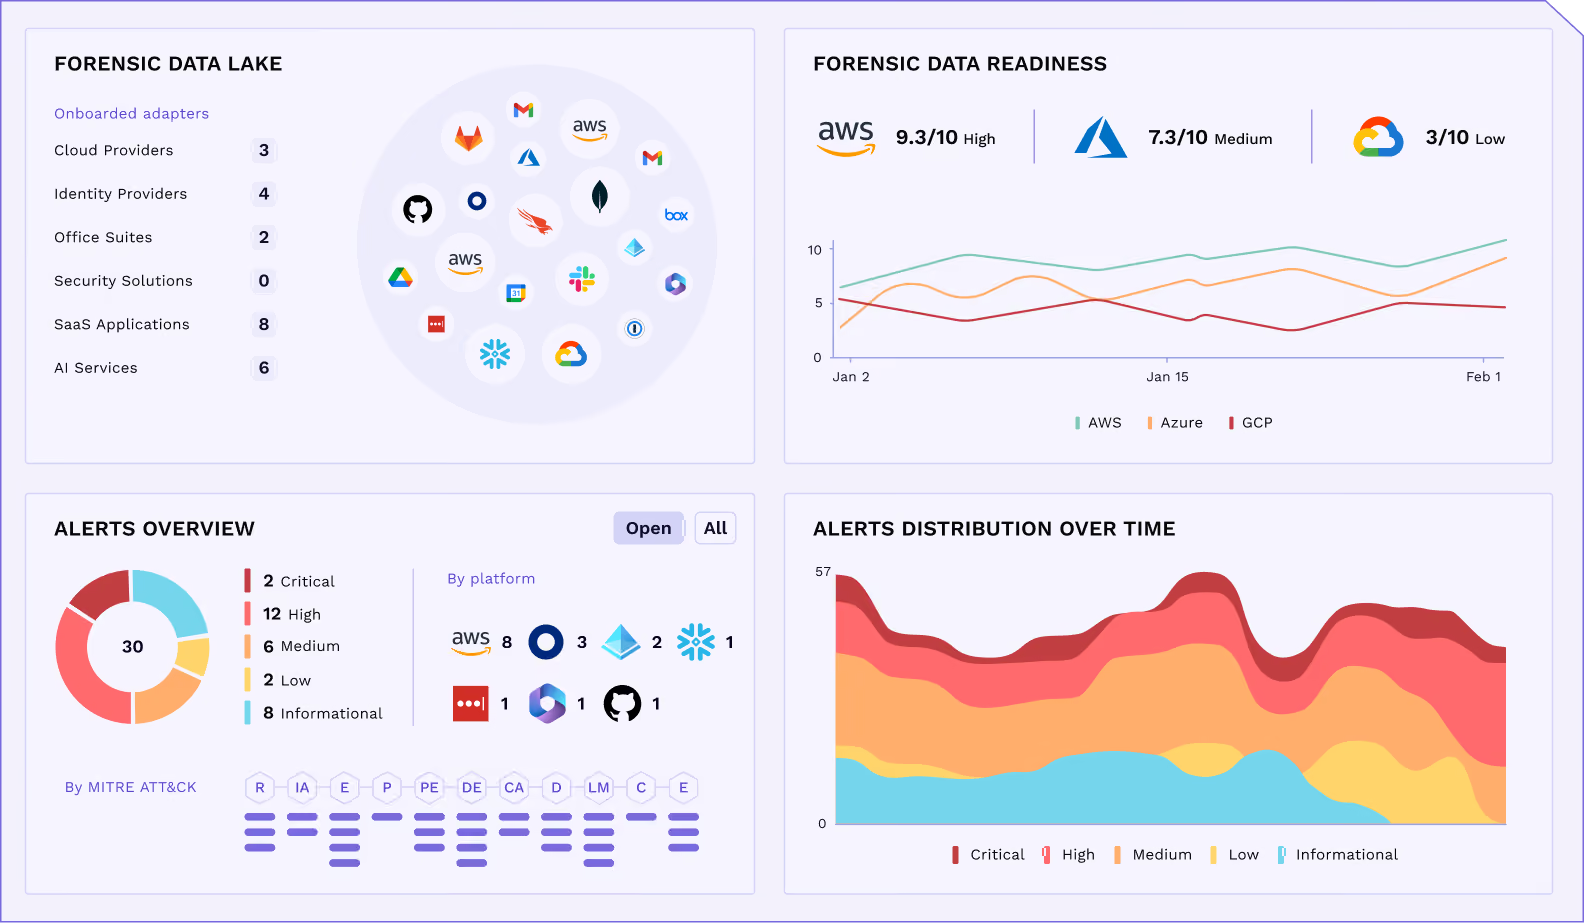
See every AI agent act across cloud, SaaS, identity, and AI—not as scattered fragments, but as one coherent, living system. Catch configuration drift and privilege escalation the moment they happen.
Trace the full story
Reconstruct every agent action, log, and signal into a unified sequence. Decode the moment legitimate behavior turns malicious.

Cut the infiltration chain
Sever a rogue agent’s momentum the moment it turns—revoking the token, quarantining the identity, and containing the attack before impact takes hold.

OUR AI AGENT SECURITY
Powered by Mitiga’s Cloud Security Data Lake, Mitiga AI Agent Security gives you command over every agent in your environment – discovered, governed, and stopped before it matters.
Mitiga collects and triages every AI agent activity and behavior automatically, turning alert floods into clear priorities so your SOC sees the full attack story at once and leads every response, instead of chasing it after a SIEM search.
Supercharges threat detection and response across cloud, SaaS, identity, and AI – so AI agent and non-human identity attacks get found, stopped, and contained in runtime before they spread.
Every agent followed from trigger to tool call to the API action it took and the identity it borrowed – across cloud, SaaS, identity, and AI in one chain, so nothing slips through.

Mitiga plugs into your
Mitiga AI Agent Security correlates signals from every tool you already run – including the AI agent and non-human identity activity none of them were built to watch.
from collection to delivery, for real-time detections
of SOC workflow automated end to end
of alerts triaged, each with an auditable verdict
the signal coverage of a human-led SOC
detections maintained and continuously tuned
5.0
"Mitiga has been a great partner in helping us modernize how we protect our cloud, identity and SaaS. We use both their platform and their managed services, and together they have helped us to get ahead of threats instead of only reacting to them."
Director, IT Security and Risk Management
in the Healthcare and Biotech Industry
5.0
"I've been consistently impressed with Mitiga and the exceptional customer experience they provide. They offer high end services that most companies miss or do not have the expertise to pull off."
Chief Information Security Officer in the Services (non-Government) Industry
5.0
"We finally feel like our security posture matches the speed and complexity of our cloud-first world."
Engineer in the Software Industry
5.0
"An Incident Response customer for a few years,
excellent support when required "
Chief Information Security Officer in the Software Industry
MITIGA LABS
mitiga labs
In July 2026, an autonomous agent ran a five-day intrusion inside Hugging Face’s own infrastructure – 17,600 actions, 11 nodes rooted. We rebuilt that attack against our own platform to see what it would take to stop it.
Read the simulation →What SecOps
"When something bad happens and you need to activate Mitiga, within an hour they already have people looking at your logs for the past year or even more."
Jonathan Jaffe, CISO, Lemonade

“We know how important it is to be prepared before an incident occurs, especially in cloud infrastructure.”
Adam Fletcher, Chief Security Officer, Blackstone
"Mitiga has a very elegant solution that enables companies to respond to sophisticated attacks in their SaaS and Cloud environments immediately."
John Watters, Former COO and President, Mandiant
"When something bad happens and you need to activate Mitiga, within an hour they already have people looking at your logs for the past year or even more."
Jonathan Jaffe, CISO, Lemonade
“We know how important it is to be prepared before an incident occurs, especially in cloud infrastructure.”
Adam Fletcher, Chief Security Officer, Blackstone
"Mitiga has a very elegant solution that enables companies to respond to sophisticated attacks in their SaaS and Cloud environments immediately."
John Watters, Former COO and President, Mandiant
explore the world of